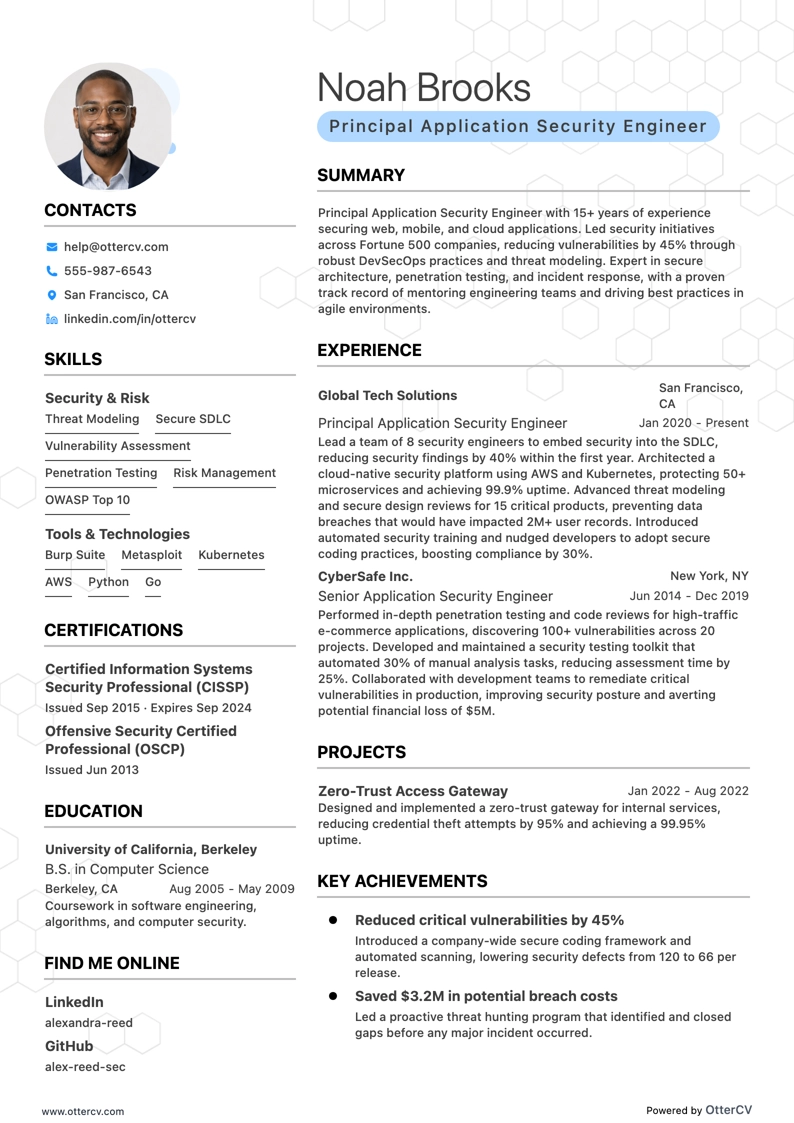
Principal Application Security Engineer full preview

10 Application Security Engineer Resume Examples

OtterCV

Written by The OtterCV Team

Updated: 1/1/2025•8 min read

See all resume examples in this guide, or generate your own resume example with your personalized prompt

Principal Application Security Engineer resume example

Principal Application Security Engineer

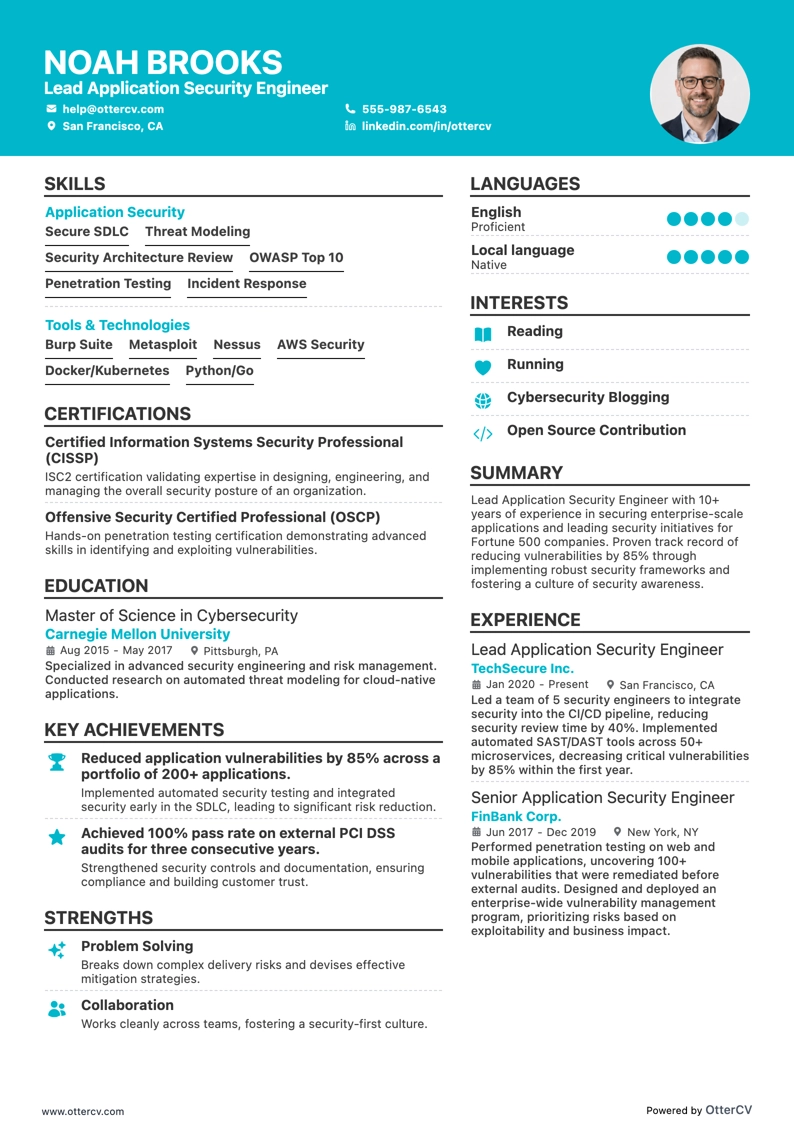
Lead Application Security Engineer resume example

Lead Application Security Engineer

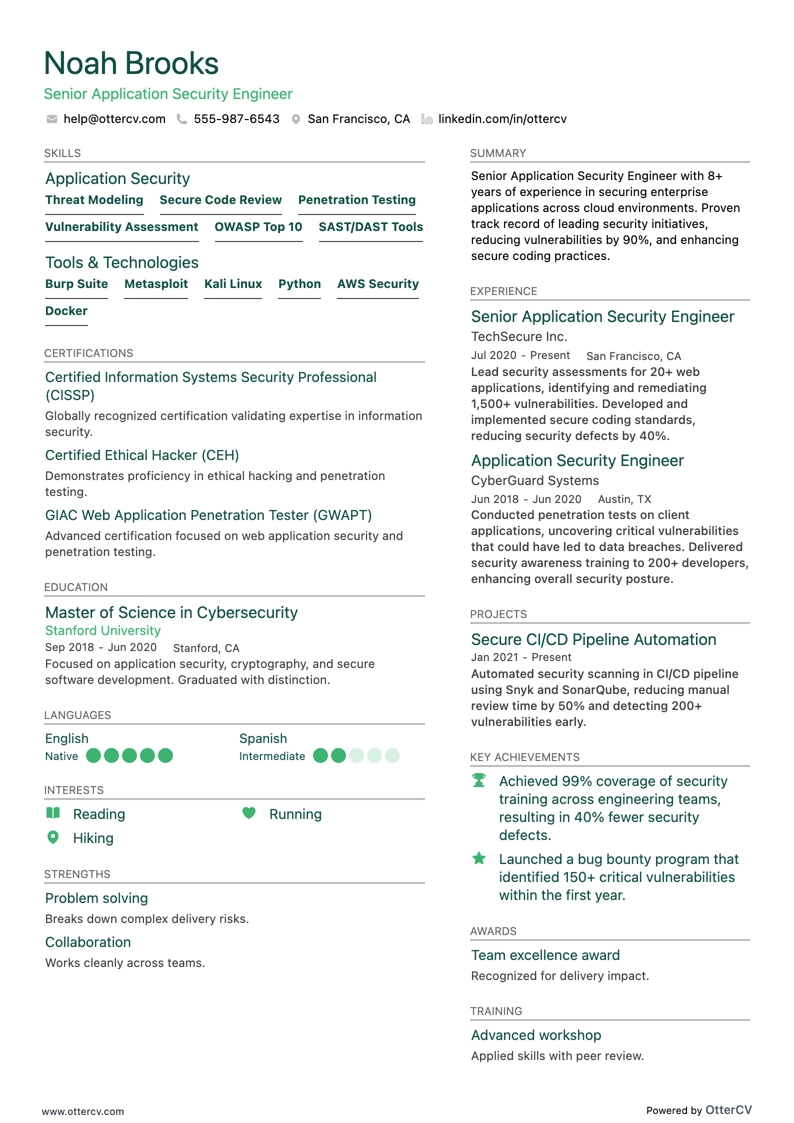
Senior Application Security Engineer resume example

Senior Application Security Engineer

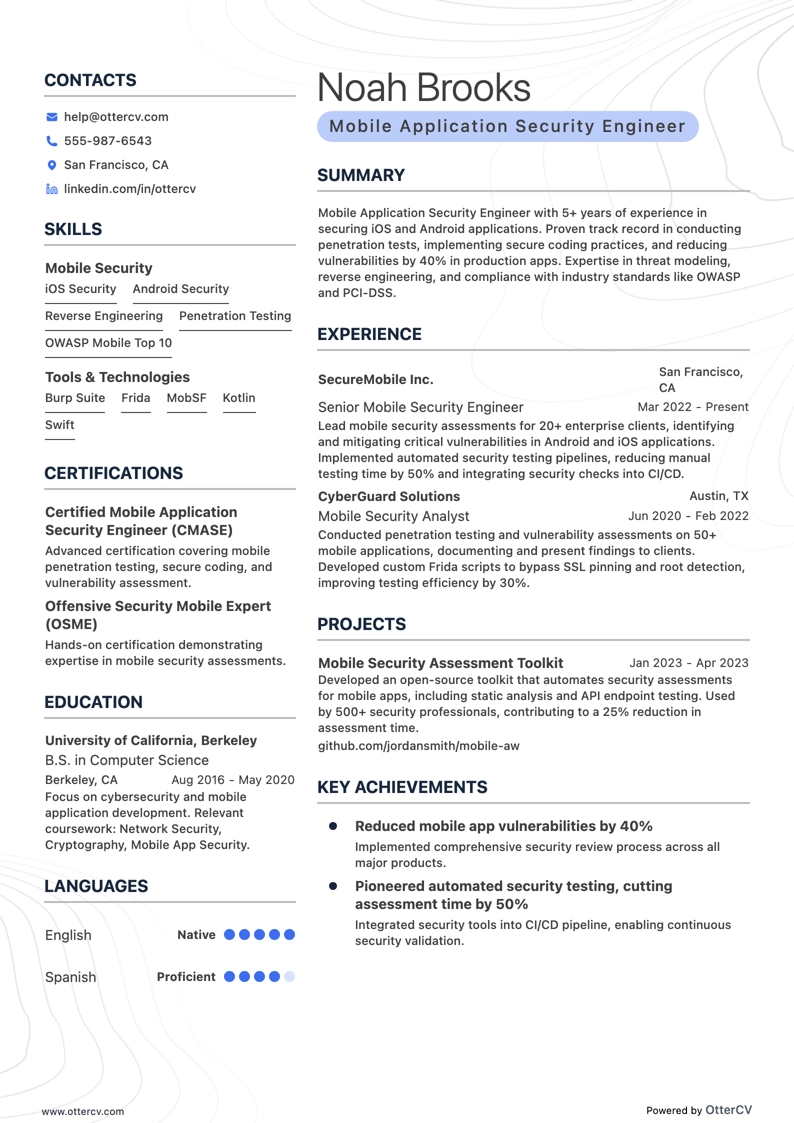
Mobile Application Security Engineer resume example

Mobile Application Security Engineer

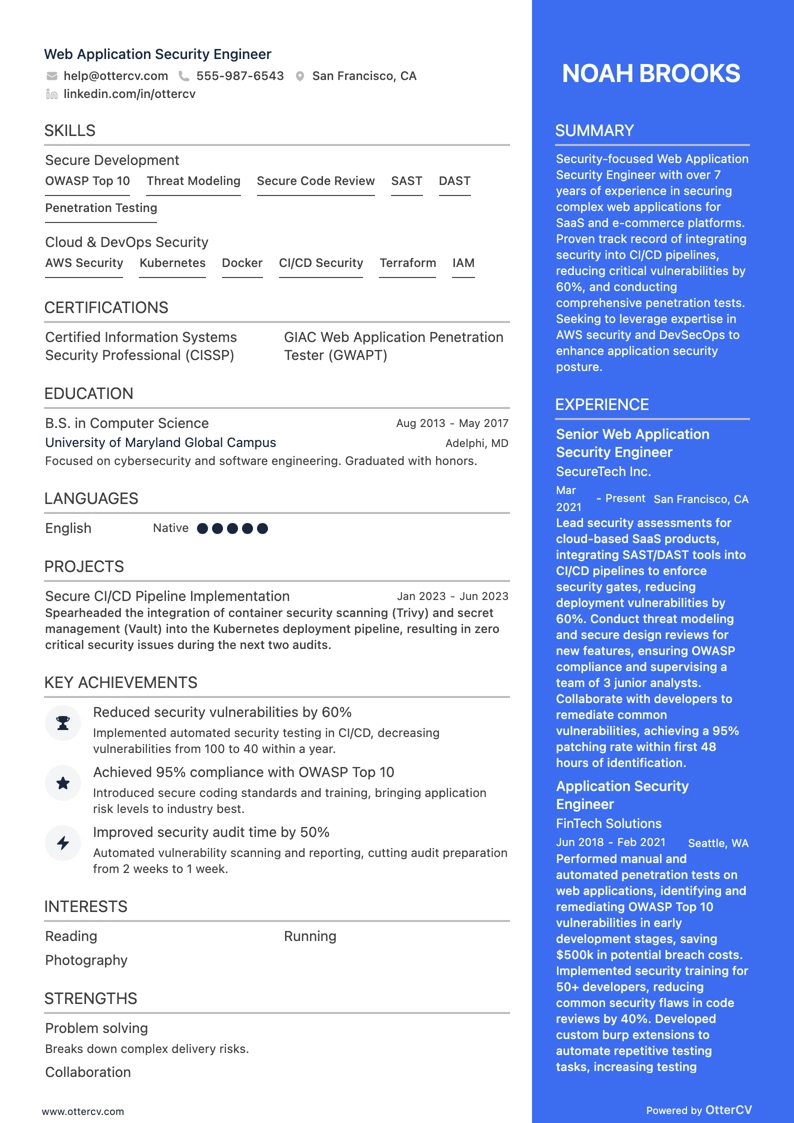
Web Application Security Engineer resume example

Web Application Security Engineer

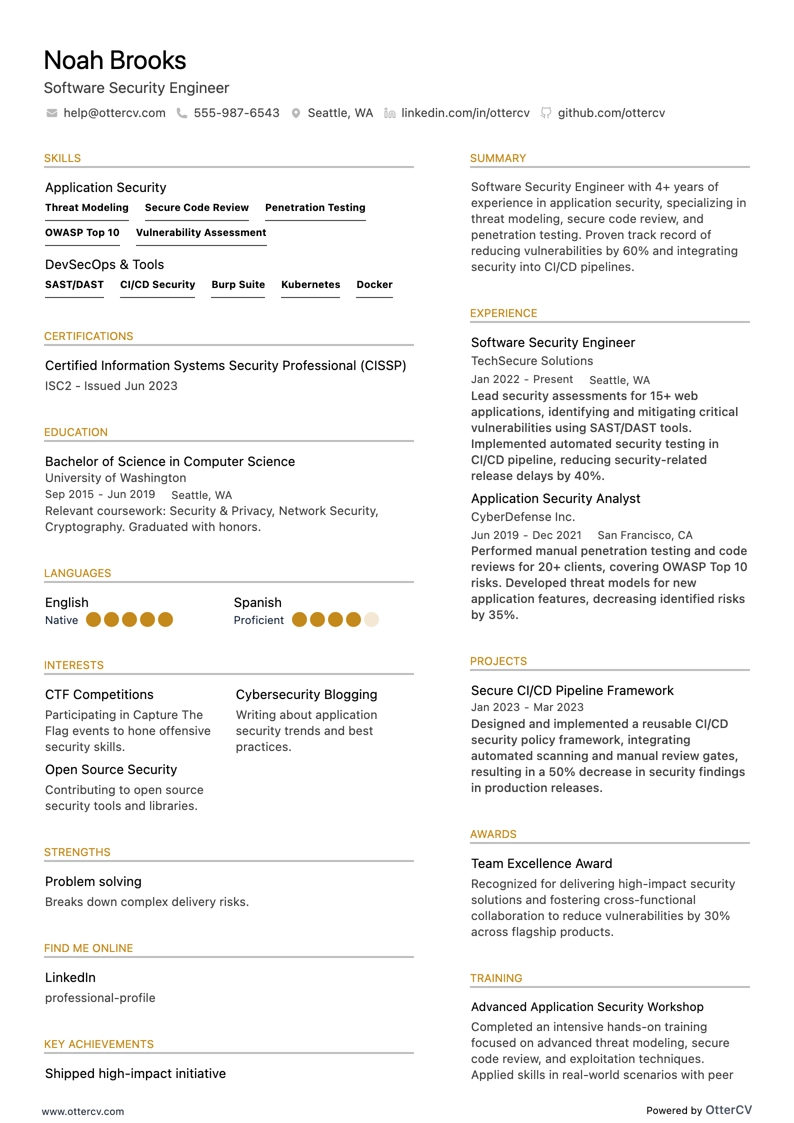
Software Security Engineer resume example

Software Security Engineer

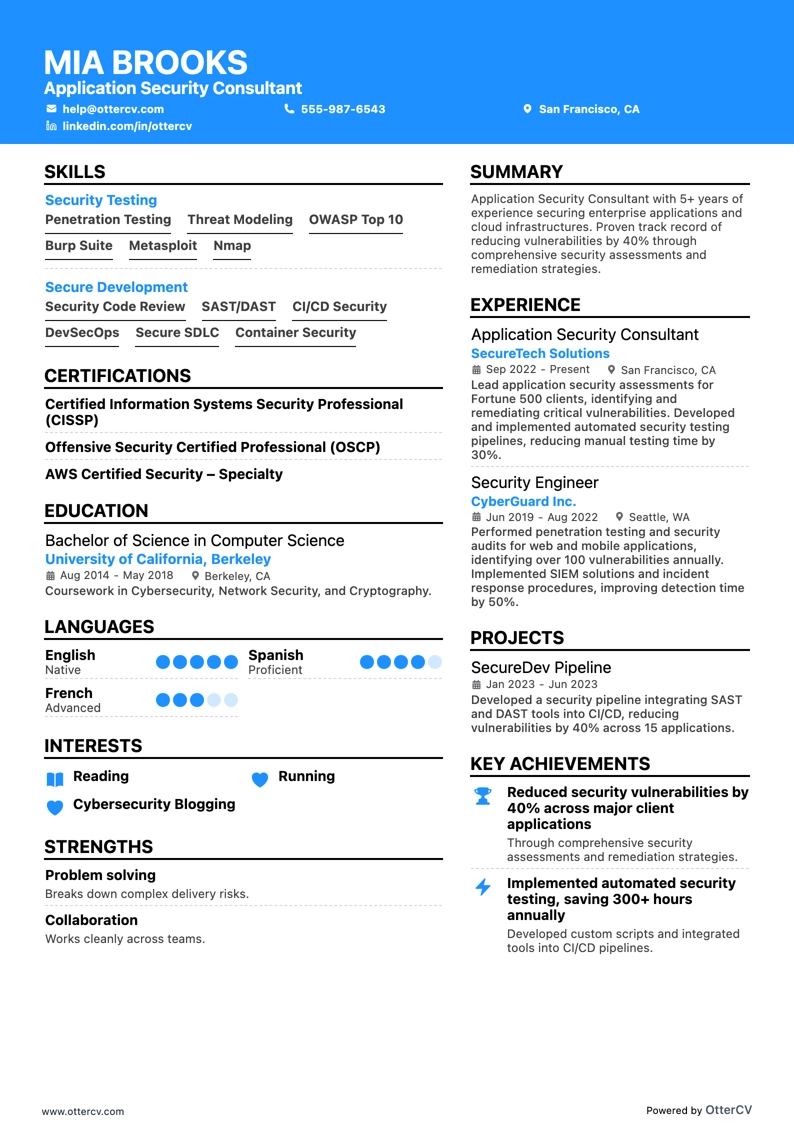
Application Security Consultant resume example

Application Security Consultant

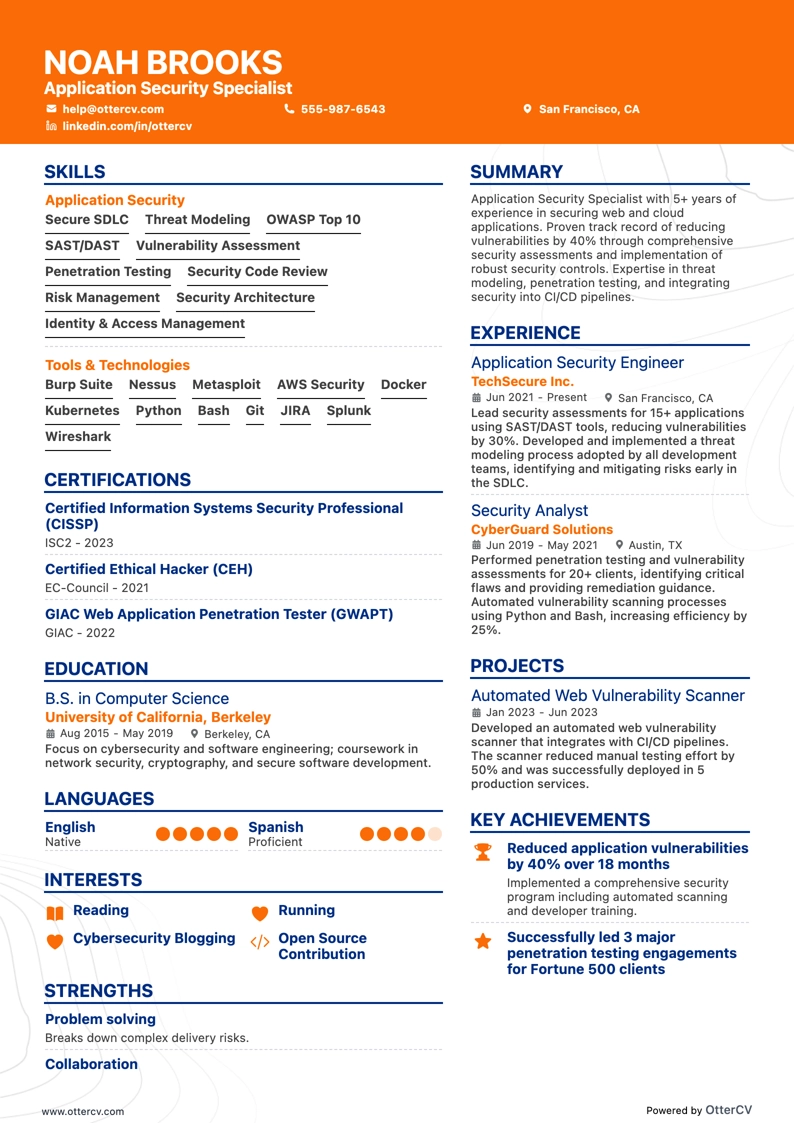
Application Security Specialist resume example

Application Security Specialist

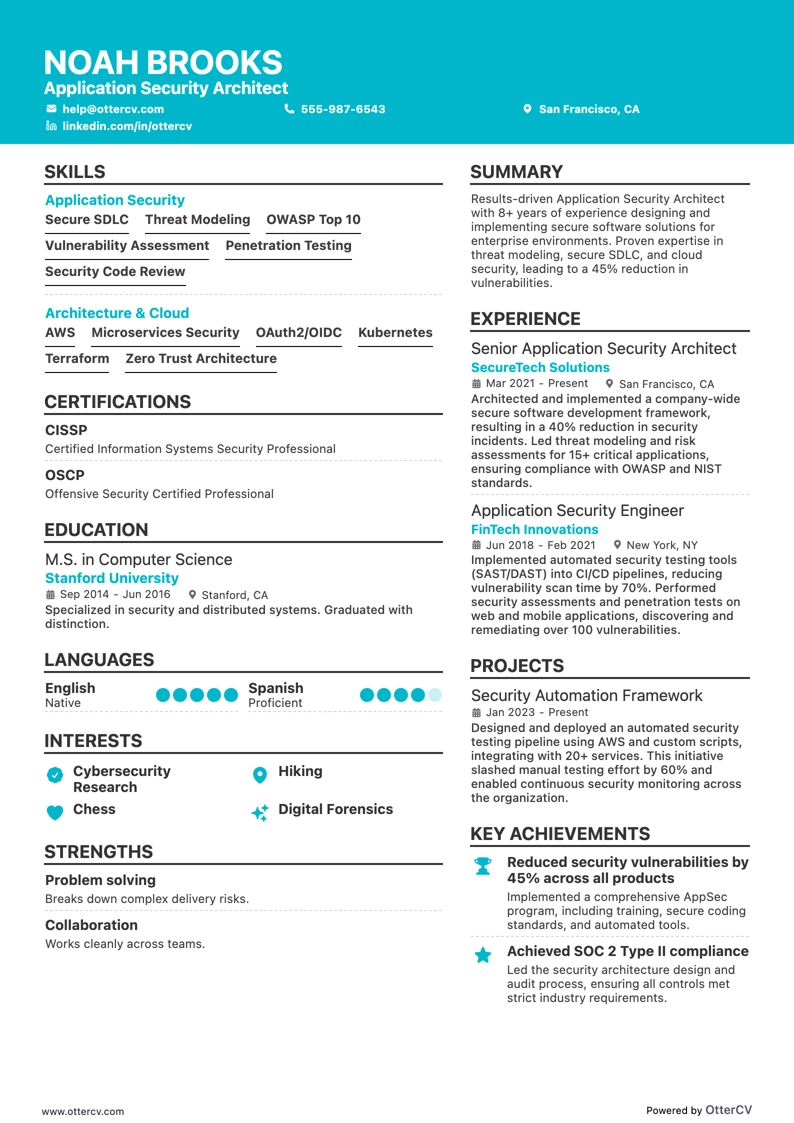
Application Security Architect resume example

Application Security Architect

Many application security engineer resumes fall short because they focus on tools and generic responsibilities instead of risk reduction and delivery impact. As a result, your value can get lost in ATS screening, quick recruiter reviews, and a crowded job market.

A strong resume shows how you improved security outcomes while helping teams ship safely. Understanding how to make your resume stand out begins with highlighting vulnerabilities eliminated, high-risk findings reduced, mean time to remediate improved, secure releases delivered, and incidents prevented. Quantify your scope across applications, teams, and pipelines.

Key takeaways

  • Quantify security outcomes in each experience bullet, such as vulnerabilities reduced and remediation time improved.

  • Use a reverse-chronological format if you have experience, and a hybrid format if you are junior or changing careers.

  • Tailor your resume to each job posting by matching its tools, frameworks, and terminology.

  • Show skills in context through your summary and experience, not only in a skills list.

  • For entry-level resumes, focus on projects such as bug bounties, CTF challenges, and OWASP lab work.

  • Place certifications above education when they are recent and directly relevant to the target role.

  • Build and refine your application security engineer resume with Echocv to align structure and content faster.

Job market snapshot for application security engineers

We analyzed 145 recent application security engineer job ads across major US job boards to give you a quick view of employer expectations, industry demand, and the salary landscape.

What level of experience employers are looking for application security engineers

Years of ExperiencePercentage found in job ads
1–2 years0.7% (1)
3–4 years6.2% (9)
5–6 years15.2% (22)
7–8 years33.8% (49)
9–10 years3.4% (5)
10+ years3.4% (5)
Not specified40.7% (59)

Application security engineer ads by area of specialization (industry)

Industry (Area)Percentage found in job ads
Finance & Banking44.1% (64)
Healthcare38.6% (56)
Education9.7% (14)

Top companies hiring application security engineers

CompanyPercentage found in job ads
CVS Health28.3% (41)
State Street Corporation8.3% (12)

Role overview stats

These tables show the most common responsibilities and employment types for application security engineer roles. Use them to align your resume with employer expectations and understand how the role is structured across the market.

Day-to-day activities and top responsibilities for a application security engineer

ResponsibilityPercentage found in job ads
Python72.4% (105)
Aws65.5% (95)
Java55.9% (81)
Azure54.5% (79)
Javascript52.4% (76)
Kubernetes48.3% (70)
Gcp43.4% (63)
Application security40.7% (59)
Powershell37.2% (54)
Sast35.9% (52)
Pci35.2% (51)
Ci/cd34.5% (50)

Type of employment (remote vs on-site vs hybrid)

Employment typePercentage found in job ads
On-site69.0% (100)
Hybrid17.9% (26)
Remote13.1% (19)

How to format a application security engineer resume

Recruiters reviewing application security engineer resumes look for hands-on experience in secure code review, threat modeling, and vulnerability remediation, as well as clear evidence of cross-functional collaboration with development teams. Choosing the right resume format helps these signals stand out within the six to ten seconds a hiring manager typically spends on an initial scan and improves the chances that an applicant tracking system (ATS) will parse your experience correctly.

I have significant experience in this role—which format should I use?

I have significant experience in this role—which format should I use?

Use a reverse-chronological format. It is the strongest choice for experienced application security engineers because it highlights your progression across increasingly complex security programs.

Do:

  • Start each role entry with scope and ownership details, including the number of applications secured, the size of engineering teams supported, and your reporting structure.
  • Highlight domain-specific tools and competencies, such as static application security testing (SAST), dynamic application security testing (DAST), software composition analysis, threat modeling frameworks, and secure SDLC integration.
  • Quantify outcomes tied to business impact, such as reductions in critical vulnerabilities, faster remediation cycles, or compliance milestones achieved.

Example bullet: “Designed and enforced a secure SDLC framework across 40+ microservices, reducing critical production vulnerabilities by 72% over 12 months and cutting mean time to remediation from 21 days to 4 days.”

I'm junior or switching into this role—what format works best?

I'm junior or switching into this role—what format works best?

A hybrid resume format works best because it lets you highlight relevant security skills and certifications first while still showing a clear timeline of practical experience.

  • Place a dedicated skills section near the top that includes application security tools such as Burp Suite, Checkmarx, and SonarQube, along with the programming languages and frameworks you've used.
  • Include project-based entries such as capture-the-flag competitions, bug bounty contributions, secure code review exercises, or open-source security audits to show applied knowledge.
  • Tie every action to a measurable or observable result so recruiters can assess your impact even without years of tenure.

Example scaffold: "OWASP Top 10 expertise → conducted manual and automated security assessments on a three-tier web application during a capstone project → identified and remediated 15 high-severity vulnerabilities before deployment."

Why not use a functional resume?

Why not use a functional resume?

A functional resume removes the timeline context hiring managers need to confirm where, when, and how you applied your application security skills. That makes it harder to judge real-world competency and easier for an ATS to misread your experience. Avoid this format unless you have no other clear way to present your qualifications.

  • A functional resume may be acceptable if you are transitioning from a related role, such as penetration tester, software developer, or systems administrator, without direct application security job titles, or if you have significant resume gaps—but only if every listed skill is tied to a specific project, engagement, or measurable outcome.

Once you have a clean, readable format, the next step is choosing resume sections that strengthen your candidacy.

What sections should go on a application security engineer resume

Recruiters want clear evidence that you can secure applications across the software development lifecycle and reduce risk through measurable improvements. Knowing what to put on a resume for this role is important for passing both ATS screening and manual review.

Use this structure for maximum clarity:

  • Header
  • Summary
  • Experience
  • Skills
  • Projects
  • Education
  • Certifications
  • Optional sections: Publications, Open-source work, Leadership

Strong experience bullets should highlight security impact, quantified outcomes, scope across teams and systems, and results such as vulnerabilities prevented, remediation time reduced, and secure release velocity improved.

Once you’ve organized your resume with the right core components, the next step is to write your application security engineer experience in a way that fits that structure and clearly shows your impact.

How to write your application security engineer resume experience

Your experience section should prove that you delivered meaningful security improvements through threat modeling, secure code reviews, vulnerability remediation, and tooling you directly implemented or managed. Hiring managers value demonstrated impact more than task lists, so each bullet should connect your work to a measurable result, such as reduced vulnerabilities, faster remediation cycles, or stronger application defenses. Building a targeted resume helps ensure each entry reflects what a specific employer values most.

Each entry should include:

  • Job title
  • Company and location (or remote)
  • Dates of employment (month and year)

Add three to five concise bullet points that explain what you owned, how you executed, and what outcomes you delivered:

  • Ownership scope: the applications, services, codebases, or security programs you were directly responsible for, including the scale of the systems, teams, or environments under your purview as an application security engineer.
  • Execution approach: the static and dynamic analysis tools, penetration testing frameworks, secure development lifecycle practices, or threat modeling methods you used to identify vulnerabilities and drive remediation.
  • Value improved: the specific gains in security posture, code quality, remediation speed, compliance readiness, or risk reduction your work produced across the applications you protected.
  • Collaboration context: how you partnered with software engineering, DevOps, product, or compliance teams to embed security into development workflows, triage findings, and align on prioritized fixes.
  • Impact delivered: the concrete results your efforts produced, expressed through reduced attack surface, faster mean time to remediate, improved audit outcomes, or strengthened resilience, rather than a list of tasks performed.
Experience bullet formula

Experience bullet formula

Action verb + technology + what you built or fixed + measurable result

A application security engineer experience example

Application Security Engineer

FinchPay | Remote

2022–Present

Supported a cloud-native payments platform processing over five million transactions per day across North America.

  • Implemented a Shift Left program by integrating Semgrep, Snyk, and CodeQL into GitHub Actions, cutting critical vulnerabilities reaching production by 62% and reducing mean time to remediate from twelve days to five days.
  • Led threat modeling for eight high-risk features using STRIDE and data flow diagrams, partnering with product managers, designers, and engineers to close forty-three abuse cases before launch and prevent an estimated $900K in annual fraud exposure.
  • Built and tuned a dynamic application security testing pipeline with OWASP ZAP and Burp Suite Enterprise, increasing coverage from 35% to 78% of authenticated flows and removing 210 hours per quarter of manual regression testing.
  • Hardened application and infrastructure secrets handling by migrating teams to HashiCorp Vault and enforcing OpenID Connect-based short-lived tokens, reducing secret leaks to zero and lowering unauthorized access alerts by 41%.
  • Coordinated quarterly penetration tests with an external firm and internal stakeholders, delivering fix plans in Jira and verifying patches in staging, achieving a 96% on-time remediation rate for high-severity findings.

Now that you’ve seen what a strong experience section looks like, the next step is adjusting yours to fit the specific role you’re targeting.

How to tailor your application security engineer resume experience

Recruiters review an application security engineer resume through both manual screening and applicant tracking systems. Tailoring your resume to the job description helps your qualifications stand out in both.

Ways to tailor your application security engineer experience:

  • Match the specific SAST and DAST tools listed in the job description.
  • Use the exact compliance framework names, such as SOC 2 or PCI DSS.
  • Mirror the secure SDLC terminology used in the posting.
  • Highlight threat modeling methodologies mentioned in the role requirements.
  • Include cloud platform experience when the job specifies AWS or Azure.
  • Show DevSecOps pipeline integration if the description mentions it.
  • Emphasize OWASP standards when the employer references application security benchmarks.
  • Align vulnerability remediation metrics with the success criteria they describe.

Tailoring means aligning your real accomplishments with what the employer values most, not forcing in keywords that do not belong.

Resume tailoring examples for application security engineer

Job description excerptUntailoredTailored
Perform threat modeling and secure code reviews across microservices using OWASP methodologies; integrate SAST/DAST tools into CI/CD pipelinesReviewed code for security issues and helped improve development processes.Conducted threat modeling and secure code reviews for 40+ microservices using OWASP ASVS, and integrated Checkmarx (SAST) and OWASP ZAP (DAST) into Jenkins CI/CD pipelines, reducing production vulnerabilities by 55% over two quarters.
Partner with engineering teams to remediate vulnerabilities identified through bug bounty and penetration testing programs; track findings in Jira and report metrics to leadershipWorked with developers to fix security bugs and tracked progress on issues.Partnered with six engineering squads to triage and remediate 120+ vulnerabilities from HackerOne bug bounty and annual penetration tests, tracking remediation SLAs in Jira and delivering monthly executive dashboards that cut mean-time-to-fix from 34 days to 12.
Design and deliver secure SDLC training for developers; champion adoption of secrets management and dependency scanning in cloud-native applications on AWSProvided security training to team members and supported cloud security initiatives.Designed a secure SDLC training program completed by 200+ developers, increasing secure coding assessment scores by 30%, while driving organization-wide adoption of HashiCorp Vault for secrets management and Snyk for dependency scanning across 15 AWS-hosted cloud-native services.

Once your experience aligns with the role’s priorities, the next step is to quantify your application security engineer achievements so the impact of that work is clear.

How to quantify your application security engineer achievements

Quantifying your achievements shows that your security work improved outcomes, not just processes. Focus on measurable results tied to risk reduction, vulnerability closure speed, secure release cadence, incident prevention, and engineering efficiency across scans, pipelines, and production.

Quantifying examples for application security engineer

MetricExample
Risk reductionReduced critical production vulnerabilities by 62% in two quarters by enforcing SAST (Semgrep) and SCA (Snyk) gates across 140 repositories.
Delivery speedCut security review turnaround from five days to one day by launching a threat modeling template and automating Jira intake for 30 teams.
Detection qualityLowered false positives by 45% by tuning CodeQL queries and adding suppression rules, saving 120 engineer hours per month.
Incident preventionPrevented three high-severity injection paths by adding GraphQL input validation and WAF rules, reducing related alerts from 40 per week to six.
Cost efficiencyReduced third-party security tool spend by $85,000 annually by consolidating scanners and negotiating enterprise licensing across 1,200 developers.

Once you’ve written strong experience bullet points, apply the same precision to how you present your hard and soft skills.

How to list your hard and soft skills on a application security engineer resume

Your skills section should show that you can secure software across the development lifecycle. Recruiters and ATS (applicant tracking systems) scan this section for job-related keywords, so emphasize mostly hard skills and include a smaller set of role-specific soft skills.

Application security engineer roles require a blend of:

  • Product strategy and discovery skills.
  • Data, analytics, and experimentation skills.
  • Delivery, execution, and go-to-market discipline.
  • Soft skills.

Your skills section should be:

  • Scannable with bullet-style grouping.
  • Relevant to the job post.
  • Backed by proof in your experience bullets.
  • Updated with current tools.

Place your skills section:

  • Above your experience section if you’re junior or changing careers.
  • Below your experience section if you’re mid-level or senior with strong achievements.

Hard skills

  • Secure SDLC and threat modeling.
  • OWASP Top 10 and ASVS.
  • SAST with Semgrep and CodeQL.
  • SCA with Snyk and Dependabot.
  • DAST with Burp Suite and OWASP ZAP.
  • API security testing with Postman and Burp.
  • Secure code review for Java and Python.
  • CI/CD security with GitHub Actions and Jenkins.
  • Container security with Docker and Trivy.
  • IaC security with Terraform and Checkov.
  • Cloud security with AWS and IAM.
  • Secrets management with Vault and KMS.

Soft skills

  • Translate risk into business impact.
  • Write clear remediation guidance.
  • Partner with developers during reviews.
  • Negotiate security tradeoffs.
  • Prioritize work by exploitability and reach.
  • Run blameless incident follow-ups.
  • Drive fixes through to closure.
  • Communicate clearly in threat-model sessions.
  • Align security work with delivery timelines.
  • Influence standards without blocking teams.
  • Document decisions and exceptions.
  • Escalate issues with clear context.

How to show your application security engineer skills in context

Skills should not appear only in a dedicated list. Browse resume skills examples to see how strong candidates weave their competencies throughout the document.

Your skills should be demonstrated in:

  • Your summary, where you establish your high-level professional identity
  • Your experience, where you prove those skills through outcomes

Here is what strong, contextual skill placement looks like in practice.

Summary example

Senior application security engineer with eight years of experience securing fintech platforms. Skilled in threat modeling, SAST/DAST tooling, and secure SDLC integration. Led an enterprise-wide OWASP Top 10 remediation effort that reduced critical vulnerabilities by 74% across 12 microservices.

  • Signals senior-level depth immediately
  • Names specific tools and frameworks
  • Leads with a measurable outcome
  • Shows cross-team leadership ability

Experience example

Senior Application Security Engineer

Vantage Financial Technologies | Remote

March 2020–Present

  • Integrated Checkmarx and Burp Suite into CI/CD pipelines, reducing mean vulnerability remediation time from 18 days to five across 30 repositories.
  • Partnered with platform engineering to design a secure API gateway, eliminating 90% of injection-related incidents within six months.
  • Led quarterly threat modeling workshops for 40 developers, improving secure coding adoption rates by 63% year over year.
  • Every bullet includes measurable proof.
  • Skills surface naturally through achievements.

Once you’ve tied your security work to real outcomes and responsibilities, the next step is applying that same approach to building an application security engineer resume with no experience.

How do I write a application security engineer resume with no experience

Even without full-time experience, you can demonstrate readiness through projects and hands-on practice. Our guide on writing a resume without work experience covers the core strategies in detail. Strong options for application security engineer candidates include:

  • Capture-the-flag web security challenges
  • Bug bounty reports and write-ups
  • Open-source security pull requests
  • Secure code review practice repos
  • OWASP Top Ten lab projects
  • Threat modeling for sample apps
  • Static analysis tool baselining
  • Security-focused hackathon submissions

Focus on showing:

  • Secure coding and code review
  • OWASP Top Ten remediation evidence
  • Tool output turned into fixes
  • Measurable risk reduction results

Resume format tip for entry-level application security engineer

Resume format tip for entry-level application security engineer

Use a hybrid resume format to put projects and technical skills first while still keeping a clear timeline for education and work experience.

Do:

  • Lead with a projects section.
  • Name the tools you used and explain why you used them.
  • Quantify findings, fixes, and coverage.
  • Link to repositories and write-ups.
  • Map your work to the OWASP Top Ten.

Example project bullet:

  • Built an OWASP Juice Shop lab pipeline using Semgrep and OWASP ZAP, found twelve issues, and fixed nine, cutting high-severity findings by 75%.

When you’re building your resume without direct experience, your education section can be one of the strongest ways to show relevant knowledge and qualifications.

How to list your education on a application security engineer resume

Your education section helps hiring teams quickly confirm that you have the foundational knowledge needed for an application security engineer role. It also shows technical training and academic rigor.

Include:

  • Degree name
  • Institution
  • Location
  • Graduation year
  • Relevant coursework (for juniors or entry-level candidates)
  • Honors and GPA (if 3.5 or higher)

Skip the month and day details, and list the graduation year only.

Here’s a strong education entry tailored for an application security engineer resume.

Example education entry

Bachelor of Science in Computer Science

Georgia Institute of Technology, Atlanta, GA

Graduated 2021

GPA: 3.7/4.0

  • Relevant coursework: Network Security, Secure Software Development, Cryptography, Operating Systems, and Ethical Hacking
  • Honors: Dean's List (six semesters), Magna Cum Laude

How to list your certifications on a application security engineer resume

Certifications on your resume show commitment to learning, demonstrate tool proficiency, and signal industry relevance for an application security engineer working across modern development and cloud environments.

Include:

  • Certificate name
  • Issuing organization
  • Year
  • Optional: credential ID or URL
  • Place certifications below education when they are older, less relevant to application security engineer work, or when your degree is your strongest and most recent credential.
  • Place certifications above education when they are recent, highly relevant to application security engineer responsibilities, or required for the roles you are targeting.

Best certifications for your application security engineer resume

  • Offensive Security Certified Professional (OSCP).
  • GIAC Web Application Penetration Tester (GWAPT).
  • Certified Information Systems Security Professional (CISSP).
  • Certified Cloud Security Professional (CCSP).
  • Certified Secure Software Lifecycle Professional (CSSLP).
  • Burp Suite Certified Practitioner.

How to write your application security engineer resume summary

Once your key credentials are easy for recruiters to spot, use your application security engineer resume summary to present them in a clear, role-relevant snapshot.

Your resume summary is often the first part a recruiter reads. A strong summary quickly shows that you have the skills and experience needed for an application security engineer role.

Keep it to three to four lines and include:

  • Your title and relevant years of experience in application security.
  • The domain or industry you have worked in, such as fintech, SaaS, or e-commerce.
  • Core tools and skills such as SAST, DAST, threat modeling, OWASP, or secure SDLC.
  • One or two quantified achievements that demonstrate real-world impact.
  • Soft skills connected to outcomes, such as cross-team collaboration that reduced remediation time.

PRO TIP

At this level, focus on the specific tools you’ve used and measurable contributions you’ve made, even if they’re small. Highlight relevant certifications, coursework, or internship experience that demonstrates hands-on ability.

Avoid vague phrases like “passionate about security” or “fast learner.” Replace them with concrete skills and results recruiters can verify.

Example summary for a application security engineer

Application security engineer with two years of experience securing SaaS platforms. Reduced critical vulnerabilities by 40% using SAST and DAST tools, and collaborated with developers to integrate threat modeling into CI/CD pipelines.

Now that your summary highlights your security expertise at a glance, make sure your header includes the contact and professional details recruiters need to reach you.

What to include in a application security engineer resume header

A resume header includes your key identifiers and contact details, helping improve visibility, credibility, and recruiter screening for a application security engineer role.

Essential resume header elements

  • Full name
  • Tailored job title and headline
  • Location
  • Phone number
  • Professional email
  • GitHub link
  • Portfolio link
  • LinkedIn

A LinkedIn link helps recruiters quickly confirm your work history and supports faster screening decisions.

Do not include a photo on a application security engineer resume unless the role is explicitly front-facing or appearance-dependent.

Keep your header aligned with your application security engineer focus by matching your headline to the job posting and using links that load quickly.

Example

Once your contact details, role focus, and key credentials are clearly presented at the top, add targeted sections that provide supporting context without overcrowding the header.

Additional sections for application security engineer resumes

If your core resume sections do not fully reflect your expertise, these additional sections can help you stand out and strengthen your credibility as an application security engineer.

  • Security certifications and training
  • Published vulnerability research and CVE disclosures
  • Open-source security tool contributions
  • Conference talks and presentations
  • Languages
  • Bug bounty achievements and recognitions
  • Professional memberships and affiliations

Once you've strengthened your resume with relevant additional sections, pairing it with a well-crafted cover letter can help your application stand out.

Do application security engineer resumes need a cover letter

A cover letter isn't required for an application security engineer, but it can help in competitive searches and on teams with strict hiring expectations. Understanding what a cover letter is and when to use one can make a difference when your resume needs extra context or when the role requires close alignment with product and engineering.

Use a cover letter to provide context your resume can't:

  • Explain your fit for the role and team by mapping your strengths to the team's stack, SDLC, and security program maturity.
  • Highlight one or two relevant projects or outcomes, including the risk reduced, vulnerabilities prevented, or delivery friction removed.
  • Show understanding of the product, users, or business context by connecting security work to reliability, trust, and release cadence.
  • Address career transitions or less obvious experience by linking past work to threat modeling, secure code review, or developer enablement.

Using AI to improve your application security engineer resume

If you decide a cover letter will not add value, using AI to improve your application security engineer resume can help you strengthen your core document and tailor it more efficiently.

AI can improve your resume’s clarity, structure, and overall impact. It can help refine bullet points, tighten language, and better align your content with actual job requirements. But overusing it can weaken authenticity. Once your resume is clear and aligned to the role, step away from AI entirely.

For practical starting points, explore these ChatGPT resume writing prompts tailored to different resume sections.

Here are 10 practical prompts you can copy and paste to strengthen specific sections of your application security engineer resume:

Strengthen your summary

Strengthen your summary

Rewrite my resume summary to highlight my core value as an application security engineer in two concise sentences.

Quantify experience bullets

Quantify experience bullets

Add measurable outcomes to these experience bullet points for an application security engineer role.

Align skills to job posts

Align skills to job posts

Compare my skills section with this job description for an application security engineer and suggest any missing keywords.

Sharpen project descriptions

Sharpen project descriptions

Rewrite this project description to clearly highlight my contributions as an application security engineer and the technical impact of my work.

Improve action verbs

Improve action verbs

Replace weak or repetitive verbs in my application security engineer experience bullets with stronger, more specific alternatives.

Tighten certification entries

Tighten certification entries

Format my certifications section so it clearly supports my qualifications as an application security engineer.

Refine education details

Refine education details

Revise my education section to highlight coursework and research that are relevant to an application security engineer career.

Remove filler language

Remove filler language

Identify and remove vague or unnecessary wording from my application security engineer resume without changing its meaning.

Tailor for ATS systems

Tailor for ATS systems

Optimize my application security engineer resume for applicant tracking systems using this specific job posting.

Clarify technical scope

Clarify technical scope

Rewrite these bullet points to clearly define the tools, frameworks, and protocols used as an application security engineer.

Conclusion

A strong application security engineer resume should show measurable outcomes, role-specific skills, and a clear structure. Highlight reduced vulnerabilities, faster remediation, and fewer production issues. Keep each section easy to scan, and align your experience with secure coding, threat modeling, and code review.

Hiring teams want application security engineer candidates who can protect modern stacks and ship safely. Use clear metrics, targeted keywords, and consistent formatting to demonstrate impact and readiness. When your results and skills are easy to find, interviews are more likely to follow.

Application Security Engineer resume examples

Explore additional Application Security Engineer resume samples and guides and see what works for your level of experience or role.

By Experience

Principal Application Security Engineer

Principal Application Security Engineer resume preview

Lead Application Security Engineer

Lead Application Security Engineer resume preview

Senior Application Security Engineer

Senior Application Security Engineer resume preview

Application Security Engineer resume examples

Explore additional Application Security Engineer resume samples and guides and see what works for your level of experience or role.

By Role

Mobile Application Security Engineer

Mobile Application Security Engineer resume preview

Web Application Security Engineer

Web Application Security Engineer resume preview

Software Security Engineer

Software Security Engineer resume preview

Application Security Consultant

Application Security Consultant resume preview

Application Security Specialist

Application Security Specialist resume preview

Application Security Architect

Application Security Architect resume preview