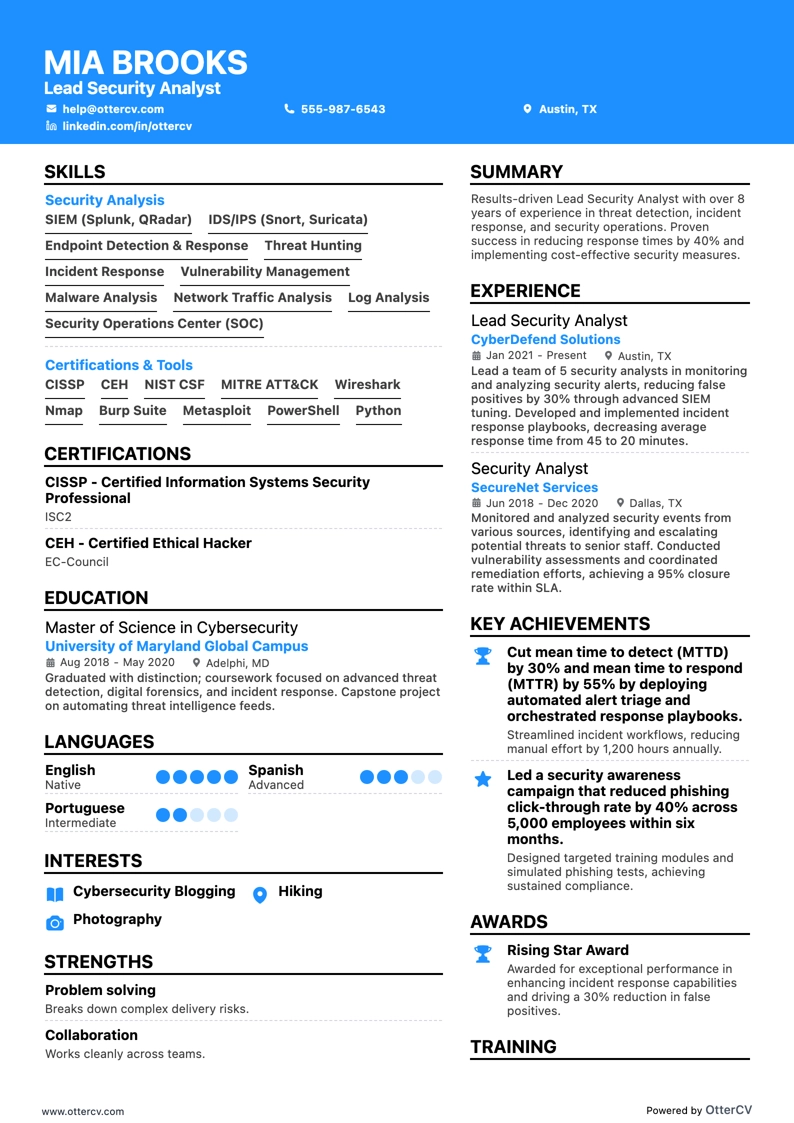
Lead Security Analyst full preview

19 Security Analyst Resume Examples

OtterCV

Written by The OtterCV Team

Updated: 4/13/2023•8 min read

See all resume examples in this guide, or generate your own resume example with your personalized prompt

Lead Security Analyst resume example

Lead Security Analyst

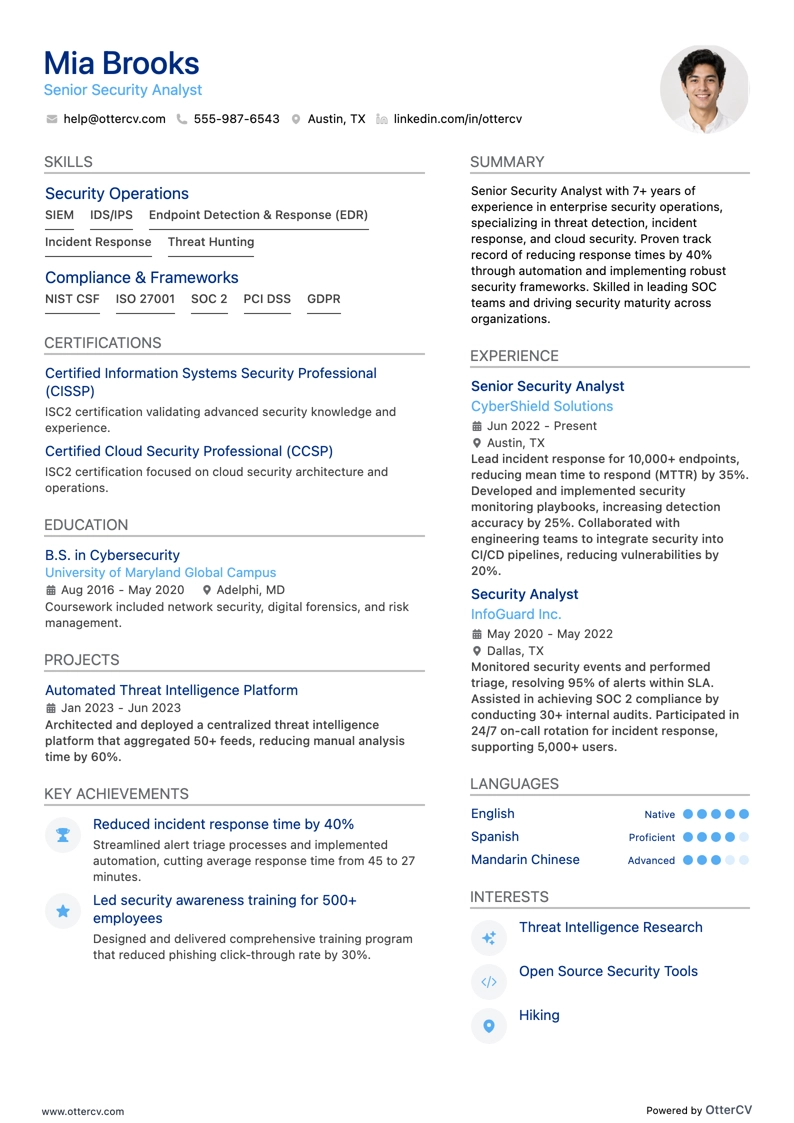
Senior Security Analyst resume example

Senior Security Analyst

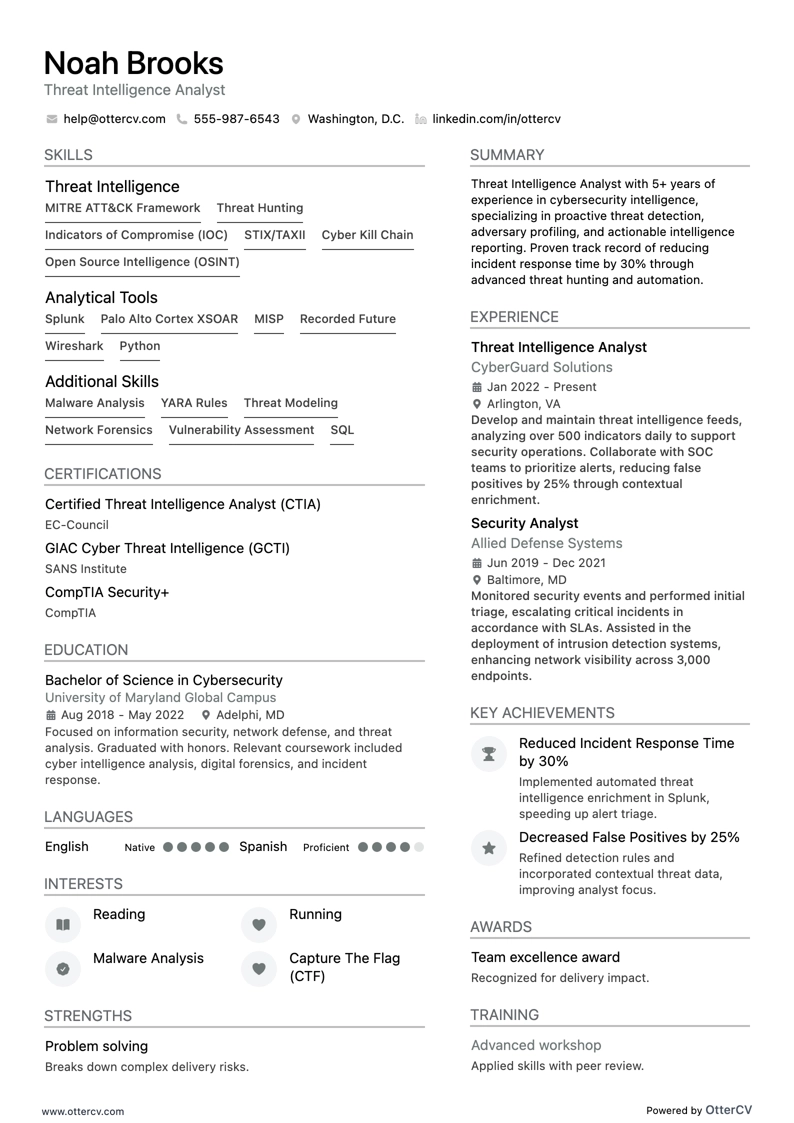
Threat Intelligence Analyst resume example

Threat Intelligence Analyst

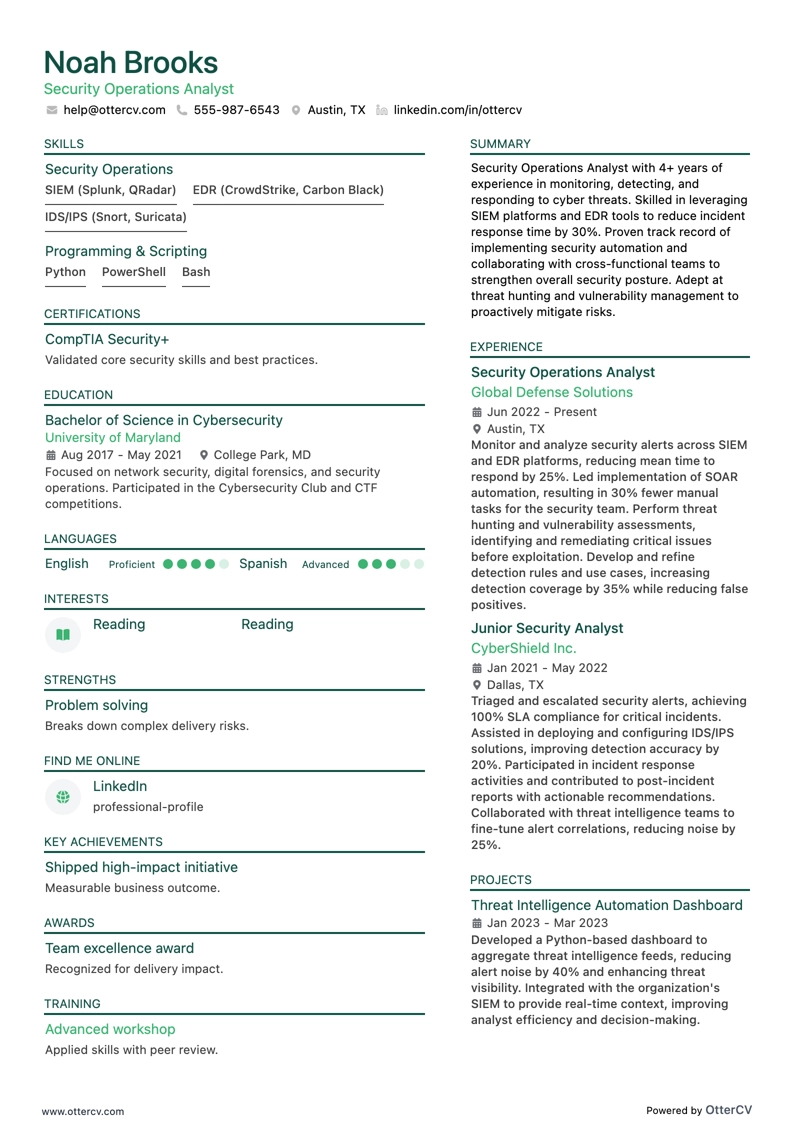
Security Operations Analyst resume example

Security Operations Analyst

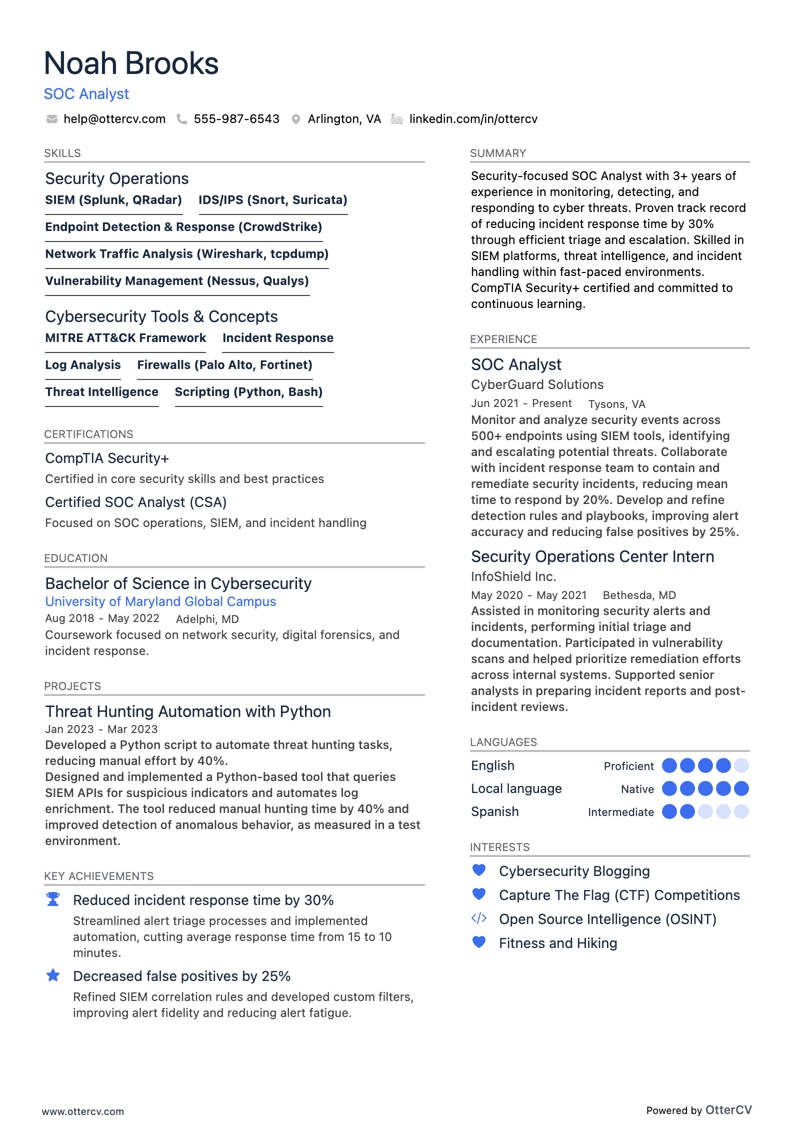
SOC Analyst resume example

SOC Analyst

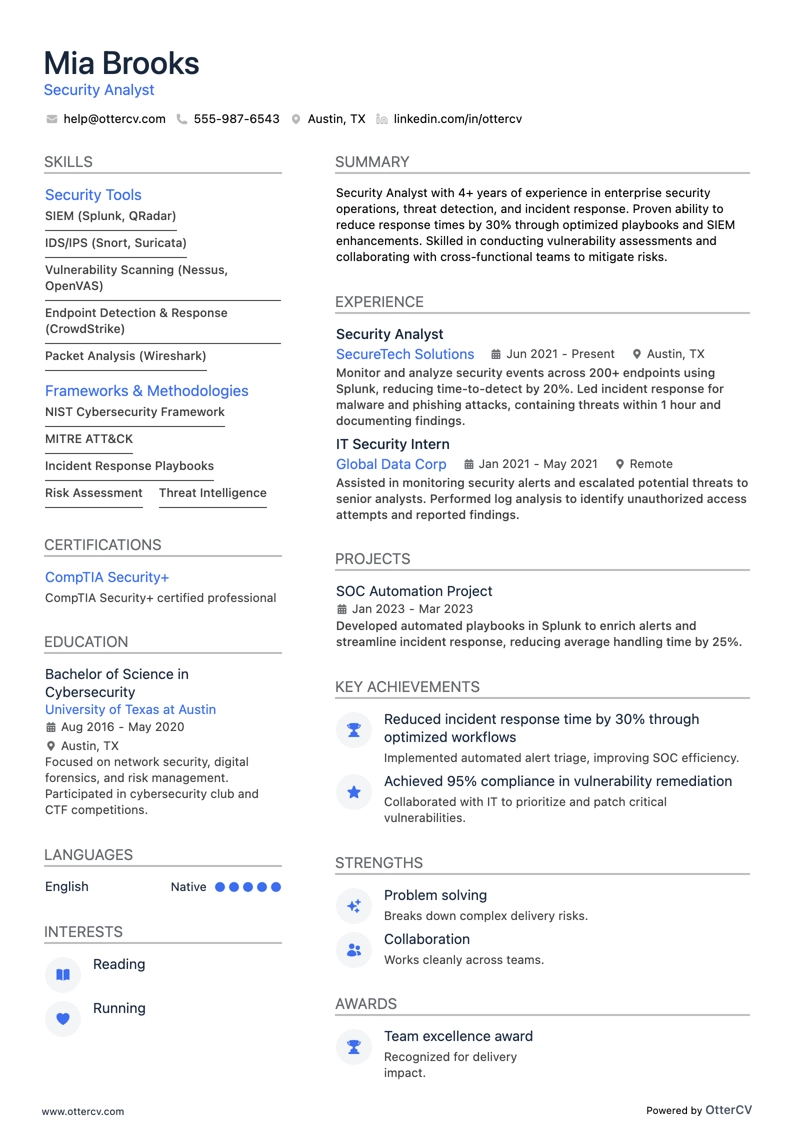
Security Analyst resume example

Security Analyst

As a security analyst, you are the frontline that turns alerts into action and threats into lessons learned. Technical skills such as SIEM, EDR, SOAR, log hunting, and scripting help you stand out, but what wins interviews is clear proof of impact: faster containment, fewer false positives, and measurable reductions in business risk.

According to the U.S. Bureau of Labor Statistics, as of November 2025, employment for information security analysts is projected to grow 29% from 2024 to 2034, which is much faster than average. That means security IT roles will remain in demand, but competition for high-profile positions will also increase.

To stay competitive, your resume should demonstrate both forensic depth and strategic thinking: how you improved detection coverage, tightened controls, shortened MTTD/MTTR, or made audits easier. In this guide, we’ll show you how to build a Security Analyst resume that leads with outcomes.

Key takeaways

  • Use reverse chronology to present a clear IT security timeline.

  • Write like a responder: keep bullets concise, action-first, and impact-driven.

  • Show how you improved detection, containment, and overall risk posture.

  • Include metrics such as MTTD, MTTR, and false-positive rates.

  • Match the exact tools in the job description, such as Splunk and XSOAR, align with metrics like alerts per day and endpoints, and reference frameworks such as MITRE and SOC 2.

  • Prioritize relevant certifications, including GCIH and Security+.

  • If you are junior, include hands-on projects to demonstrate technical readiness.

Let’s review several security analyst resumes and see what makes them compelling.

Does your current resume look like any of these examples? What weaknesses might it have? Use Echocv’s ATS Resume Checker to get a full report.

What resume format works best for a security analyst?

Use a reverse-chronological resume if you have recent SOC, DFIR, or engineering experience.

Use a hybrid format if you are junior or changing directions.

How to structure your content

Prioritize work and projects from the last two to three years.

  • Highlight incidents you handled, detections you shipped, or controls you hardened.
  • Group tools by function—SIEM, EDR, cloud, and vulnerability management—and tie them to results such as coverage, MTTR, or audit findings.
  • Use clear dates to reinforce chronology, for example, “Jun 2021 - Apr 2024”.

What sections should go on a security analyst’s resume?

  • Resume header (name, cert post-nominals, location, phone, email, LinkedIn, GitHub)
  • Professional summary (years in security, SOC tier or role, two quantified outcomes, two core strengths)
  • Work experience (a few bullet points per job, each covering scope, tech, and impact)
  • Skills (concise, scannable, and focused on technical capabilities)
  • Education (degree, institution, graduation year, GPA if above 3.5)
  • Certifications (list only certifications you hold, prioritizing recently earned ones or those requested in job ads)
  • Projects & Labs (especially helpful for juniors and detection engineers)

Now that the structure is clear, the next step is how to write each section.

How to write your security analyst resume experience section

Write experience bullet points like mini incident reports: action + tool + scope + measurable outcome. Use active subject-verb-object phrasing whenever possible.

Good example of a security analyst experience section

Security Analyst | Horizon Data Systems, Austin, TX
June 2019–Present

  • Managed detection for approximately 1,800 endpoints, reducing false positives by 45% and cutting MTTD from 2.5 hours to 28 minutes.
  • Built 16 SOAR/Sigma playbooks for phishing and lateral movement, saving 150 analyst-hours per month and reducing P1 MTTR from 90 minutes to 22 minutes.
  • Hardened AWS across CloudTrail, GuardDuty, and IAM; enforced least-privilege access and alerting, eliminating an exfiltration channel and reducing privileged anomalies by 67%.
  • Led quarterly vulnerability assessments and patching with DevOps, reducing the critical backlog by 78% and supporting SOC 2 attestation.
  • Mapped detections to MITRE ATT&CK and hunted across EDR and cloud logs; identified credential-theft activity and contained 23 compromised accounts.
  • Mentored 4 junior analysts and wrote runbooks and triage guides, increasing first-touch resolution to 62% and improving incident handovers.

Why does this experience section work?

Security experience is judged by measurable outcomes. Focus your bullets on credential abuse, vulnerability exploitation, and ransomware.

Map your actions to patterns like these:

  • How many incidents you remediated
  • How quickly you detected and contained threats
  • How you made the environment measurably safer

PRO TIP

If a job description explicitly mentions tools or frameworks such as Splunk, Sentinel, CrowdStrike, or MITRE, highlight them early in your resume.

Include them in your summary, then reinforce them with metric-driven bullets in your experience section.

The most common breach drivers in 2025 were:

  • Vulnerability exploitation reached 20% of initial access (34% YoY).
  • Ransomware appeared in 44% of breaches.
  • The human element remains ~60%.

How to quantify your impact as a security analyst

Pick two or three metrics for each role, and clearly label the scope and time period. Numbers on your resume help hiring managers understand risk reduction and time saved.

Metrics that matter most for security analysts include:

  • Detection coverage: % of ATT&CK techniques covered or rules/playbooks deployed (for example, “+17 Sigma rules; T1059, T1110 covered”).
  • MTTD/MTTR: Mean time to detect and respond for P1/P2 incidents over a quarter.
  • Vulnerability risk: % of critical CVEs remediated within SLA; median days to patch on edge/VPN devices. DBIR notes rising vulnerability exploitation, so it helps to show patch cadence.
  • Cost/risk impact: Tie wins to IBM’s benchmark. As of July 2024, average breach costs are $4.88M.
  • Signal quality: False-positive rate, alert-to-case conversion, or noisy rules you suppressed.
  • Automation: Tickets auto-enriched or resolved per week; manual minutes saved per alert.

When quantifying your experience, use an action verb, a tool or technology, and a measurable outcome.

Here’s how:

How to quantify achievements on your resume

How to quantifyExample bullet point
MTTD (Mean Time to Detect) — average time to surface a confirmed threat.“Cut average MTTD from 2.5h to 28m by deploying new Splunk detections and scheduled threat hunts.”
MTTR (Mean Time to Remediate/Contain) — average time from detection to containment or remediation.Automated containment with XSOAR + CrowdStrike, reducing P1 MTTR from 90m to 28m.
False-positive rate — percentage of alerts identified as non-threats after triage.Tuned Splunk rules and enrichment, lowering false positives by 38% and improving analyst focus.
Alerts-to-cases conversion — proportion of raw alerts that become investigated incidents or cases.Triaged over 1,200 alerts/week, increasing alerts-to-case conversion from 4% to 11%.
Analyst-hours saved — time reclaimed through automation, playbooks, or detection tuning.Built 8 SOAR playbooks that automated enrichment and containment, saving over 120 analyst-hours/month.

Need help quantifying your experience? With Echocv’s AI Bullet Point Generator, you can quickly turn regular security analyst tasks into metrics-driven statements.

Now that you know how to write your experience, make it more compelling to employers by tailoring it to the role.

How to tailor your security analyst resume experience

To create a targeted resume, mirror the employer’s language around tools, scale, metrics, and responsibilities while keeping every bullet truthful and focused on outcomes.

Here’s how:

  • Use the exact tool names and versions listed in the job ad, such as Splunk, Microsoft Sentinel, CrowdStrike Falcon, and Cortex XSOAR. ATS often matches exact tokens.
  • Match the scope and scale they describe, including endpoints, users, cloud accounts, log sources, alerts per day, and SOC tier. If the ad says “50k endpoints,” show the number of endpoints you supported.
  • Use their metrics in your bullets, such as MTTR, false positives, or alerts-to-cases, if those are how they measure performance.
  • Map your work to the frameworks they care about, including MITRE ATT&CK, NIST CSF, CIS controls, PCI, and SOC 2, and name the artifact, such as “mapped to ATT&CK” or “aligned to NIST CSF.”
  • Mirror their function words, such as “threat hunting,” “detection engineering,” “IR,” “SOAR playbooks,” and “vulnerability remediation.” Reuse the same verbs and nouns where they fit your experience.
  • Highlight the deliverables they value, including playbooks, Sigma/KQL rules, incident reports, tabletop exercises, automated containment steps, and IOC lists.

Job description from a real posting

  • Hiring a Security Analyst to defend a hybrid environment across AWS and on-prem datacenters.
  • Monitor and investigate security telemetry.
  • Create and tune detection rules and automated playbooks.
  • Drive incident response to meet aggressive MTTD and MTTR goals.
  • Use Python or PowerShell automation to accelerate containment.
  • Run proactive threat hunts across cloud and endpoint logs.
  • Help map incidents to frameworks for audits and compliance.
  • Experience with SIEM and EDR platforms is preferred.
  • Familiarity with MITRE ATT&CK, SOC 2, or NIST is preferred.

Here’s how to tailor bullet points for each of the highlighted requirements.

Resume tailoring examples for security analysts

Job description excerptUntailored bulletTailored bullet
“Monitor and investigate security telemetry.”Monitored security telemetry and investigated alerts.Monitored Splunk and EDR telemetry across ~40k endpoints; triaged ~2k alerts/day and escalated confirmed incidents, reducing false positives by 38%.
“Develop and tune detection rules and automated playbooks.”Wrote detection rules and built automated playbooks.Authored 12 SPL/KQL detection rules and 8 Cortex XSOAR playbooks to automate enrichment and containment for phishing and lateral movement, saving ~120 analyst-hours/month.
“Meet MTTD/MTTR SLAs across corporate systems.”Worked to meet MTTD and MTTR targets.Tuned detections and automated containment to cut average MTTD from 2.5h to 28m and bring P1 MTTR < 30m, meeting SOC SLAs.
“Experience with automation and scripting (Python or PowerShell).”Automated repetitive tasks using scripting.Built Python/PowerShell automation that auto-quarantined infected hosts via EDR and updated blocklists, reducing containment time by ~65%.
“Threat hunting, cloud logging, and mapping to frameworks (MITRE, SOC 2, NIST).”Performed threat hunts and supported audits.Conducted proactive hunts across CloudTrail and EDR logs, mapped findings to MITRE ATT&CK, and closed 6 audit-relevant gaps used in SOC 2/NIST evidence.

PRO TIP

Use Echocv’s One-Click Tailoring Feature to automatically match your bullet points, skills, and sections to any job description.

After all these efforts, your experience is now presented in the best possible light. Next, focus on another resume section that is essential for this role.

How to list technical skills on a security analyst resume

Technical skills help recruiters and ATS quickly see whether you can do the job.

Here’s where to place skills on your resume:

  • Experienced analysts (Tier 2–3, DFIR, detection engineers): Add a targeted technical skills section after your work experience. If you use a double-column resume, you can place it alongside your experience.
  • If you have many skills relevant to the role: Group them by category, such as SIEM, EDR, Automation, Cloud, and Forensics, so the ATS can parse them correctly.

Best technical skills for your security analyst resume

  • SIEM tools include Splunk, Microsoft Sentinel, QRadar, and LogRhythm.
  • EDR tools include CrowdStrike, Microsoft Defender, and Carbon Black.
  • SOAR and automation skills include Cortex XSOAR, Phantom, Demisto, Python, and PowerShell.
  • Detection languages include SPL, KQL, Sigma rules, and YARA.
  • Cloud logging and security tools include AWS CloudTrail, CloudWatch, Azure Monitor, and GCP Audit Logs.
  • Forensics and incident response tools include Volatility, GRR, FTK, Autopsy, Wireshark, and Zeek.
  • Threat hunting and analytics skills include TTP mapping (MITRE ATT&CK), IOC development, and telemetry analysis.
  • Vulnerability and posture skills include Nessus, Qualys, Tenable, and vulnerability remediation workflows.
  • Useful networking and protocol knowledge includes TCP/IP, DNS, proxy logs, and firewalls (conceptual).
  • Compliance and framework knowledge includes NIST CSF, CIS Controls, and SOC 2 evidence gathering.

How to integrate soft skills on a security analyst resume

Include soft skills in your summary, experience bullets, and project descriptions, and connect them to a measurable result or clear deliverable.

Examples

Here are some examples.

Summary: “Skilled communicator who keeps teams aligned and calm during high-pressure incidents.”

Experience bullet: “Coordinated with IT and Legal to ensure smooth, collaborative incident response.”

Project description: “Led a tabletop exercise, fostering open feedback and teamwork across departments.”

Soft skills in IT security are not a separate “nice-to-have” section. They show how you get things done under pressure.

We covered your experience and technical capabilities—now let’s back them up with some credentials.

How to list certifications and credentials on a security analyst resume

Certifications take priority on an IT resume because they signal readiness for security roles.

Certifications

List each certification with the following details:

  • Full certification title
  • Issuing organization
  • Year obtained (add “current” or expiration if required by the employer)

Certification entry sample:

CompTIA Security+ — CompTIA, 2025

GIAC Certified Incident Handler (GCIH) — SANS, 2025

Quick Tips

  • Place certifications near the top if the job prioritizes them or if you are changing careers.
  • Include vendor or region-specific details when relevant, such as AWS Security Specialty — AWS, to better match job requirements.
  • For certifications that expire, include the year and status, such as Active or Recertified 2024.
  • Keep each entry brief, factual, and easy to verify.

If you completed security-related bootcamps, earned CTF rankings, or took SANS courses, list them in a Projects or Professional Development section instead of presenting them as formal certifications.

How to list education on a security analyst resume

Keep your education section concise so recruiters can quickly see that you have the academic foundation for the industry.

What to include in your education section:

  • Degree
  • Institution
  • Location
  • Year of graduation
  • GPA (only if it is above 3.5 and you’re early in your career)

Education entry sample

Bachelor of Science in Cybersecurity, Georgia Institute of Technology, 2019

Associate of Science in Computer Science, Austin Community College, 2016, GPA: 3.7

If you’re early in your security career, expand the education section with relevant coursework or capstone projects such as Incident Response, Digital Forensics, Cloud Security, Network Defense, and Secure Coding.

Once the main body of your resume is complete, write the introduction to your professional persona.

How to write your security analyst resume summary

Keep your resume summary concise, confident, and focused on outcomes so hiring managers can quickly understand your operational impact.

A strong security analyst resume summary should include:

  • Your current role and years of experience
  • Your environment type or specialization, such as SOC tier, cloud, enterprise, DFIR, or detection engineering
  • Your key tools and techniques, including SIEM, EDR, SOAR, threat hunting, and scripting
  • One to two quantified results, such as MTTD/MTTR improvement, false-positive reduction, or analyst-hours saved
  • Soft skills connected to measurable outcomes

Example summary

Collaborative security analyst with 5+ years in a Tier-2 SOC protecting hybrid cloud and enterprise environments. Skilled in Splunk, Microsoft Sentinel, CrowdStrike, and XSOAR, with experience authoring detections and automated playbooks that cut MTTD from 2.5h to 28m and reduced false positives by 38%.

Known for clear incident communication, cross-team leadership, and mentoring junior analysts to improve response quality.

Why this summary works

  • Establishes experience level, security specialization, and hands-on use of industry tools.
  • Demonstrates measurable impact with concrete security outcomes.
  • Shows technical depth, business value, and interpersonal skills.

How do I write a security analyst resume with no experience?

If you’re early in your career and just starting your professional journey in IT security, you can still build a persuasive security analyst resume without years in a SOC.

Focus on showing technical readiness and investigative thinking. Highlight coursework, certifications, and hands-on labs or CTFs so hiring managers can see your foundation of technical skills and motivation.

What to include instead of full-time security analyst experience

  • Certifications: List your most relevant certifications immediately after your summary.
  • Academic projects or labs: Describe simulated IR exercises, SIEM searches you wrote, or hosted ELK/CloudTrail log pipelines used for hunts, and mention tools such as Splunk, Sentinel, CrowdStrike, Volatility, and GRR.
  • Internships/IT support roles: Highlight triage, ticket handling, basic forensics, and escalation to show transferable incident-handling experience.
  • Personal or homelab projects: Include threat-hunt writeups, detection rule repositories (Sigma/SPL/KQL), EDR playbooks, or Python automation that quarantined test hosts.
  • Volunteer work: Include pro-bono assessments, SOC help for nonprofits, or security workshops to demonstrate initiative and real-world impact.

Now that we’ve covered the essential components of a resume, it’s time to fine-tune some of the details.

Frequently asked questions for security analyst resumes

Here’s some clarity around common concerns applicants have.

What design and text formatting rules should you follow for a security analyst resume?

In short, keep your resume professional and ATS-friendly:

How should you name and save your resume file?

Use a clear filename so recruiters and ATS can find it easily.

Example: Henry_Steinberg_Security_Analyst.pdf

Export as a PDF file to preserve layout and avoid font or formatting shifts across systems.

What should a security analyst cover letter include?

Use the cover letter to share one concise, relevant incident story that connects your hands-on experience to the employer’s needs.

Focus on:

  • Why you want to work for this organization or with this tech stack.
  • A brief incident vignette covering the detection, your role and actions, the tools used, and the measurable outcome.
  • How you would apply that experience to their environment, such as SIEM, EDR, cloud, or compliance.

Keep it targeted and limited to one page, and do not repeat your resume.

How do I show career progression on a security analyst resume?

Chronology and metrics make career progression clear on IT resumes.

  • Use reverse-chronological order so promotions and ownership are easy to see.
  • Show increases in scope, such as endpoints, alerts per day, log sources, or cloud accounts.
  • Highlight new responsibilities, including IR lead work, detection engineering, or playbook ownership.

What additional sections work well on a security analyst resume?

Focus on sections that directly support your IT security skills:

  • Projects: Playbooks, detection rules, threat-hunt reports, and automation scripts.
  • Open-source/epos: Sigma/SPL/KQL rules, GitHub detection libraries, and SOAR playbooks.
  • CTF/competitions: Notable placements or relevant challenges.
  • Presentations/publications: Talks, blog posts, or whitepapers on IR and detection.
  • Clearance/legal: Active security clearance or jurisdiction-specific notes, if applicable.

Do I need specific certifications to work as a Security Analyst in the U.S.?

Not legally required, but many employers expect or prefer certifications that demonstrate practical detection and IR ability, such as Security+, CySA+, GCIH, and Splunk/Sentinel certifications.

Should I include salary expectations on my resume?

No. Leave salary figures off your resume. Use market research and interview conversations to negotiate compensation.

In conclusion, security resumes should prove impact and accountability

Treat your resume like an incident briefing: concise facts, the tools used, and measurable outcomes. Prioritize metric-first bullets that show detection coverage, response speed, and risk reduction. Mirror keywords from the job posting, including SIEM/EDR names, MITRE, SOC 2, and MTTD/MTTR, and support them with short, verifiable accomplishments.

Security Analyst resume examples

Explore additional Security Analyst resume samples and guides and see what works for your level of experience or role.

By Experience

Lead Security Analyst

Lead Security Analyst resume preview

Senior Security Analyst

Senior Security Analyst resume preview

Security Analyst resume examples

Explore additional Security Analyst resume samples and guides and see what works for your level of experience or role.

By Role

Threat Intelligence Analyst

Threat Intelligence Analyst resume preview

Security Operations Analyst

Security Operations Analyst resume preview

SOC Analyst

SOC Analyst resume preview

Security Analyst

Security Analyst resume preview